Secure Multi-Party Computation in AI
1. Definition and Core Principles of SMPC
Definition and Core Principles of SMPC
Secure Multi-Party Computation (SMPC) is a cryptographic protocol that enables multiple parties to jointly compute a function over their private inputs while keeping those inputs confidential. The fundamental goal is to ensure that no party learns anything beyond the output of the function, even if some participants are malicious or semi-honest. This property is formalized through privacy and correctness guarantees, which are central to SMPC's security model.
Mathematical Foundations
The security of SMPC relies on formal definitions from computational complexity and cryptography. A protocol is considered secure if it satisfies the following conditions for a function f computed over inputs x1, x2, ..., xn from n parties:
Here, Viewi represents the information seen by party i during the protocol execution, and Simi is a simulator that produces a computationally indistinguishable view using only the function output. The symbol ≈c denotes computational indistinguishability, meaning no polynomial-time adversary can distinguish between the real and simulated views.
Core Principles
SMPC protocols are built on three foundational principles:
- Input Privacy: No party should learn another party's private input beyond what can be inferred from the output.
- Correctness: The computed output must match the result of the function applied to the true inputs, even if some parties deviate from the protocol.
- Independence of Inputs: Parties must choose their inputs independently, without coercion or influence from others.
Adversarial Models
SMPC protocols are analyzed under different adversarial models, which define the capabilities of malicious participants:
- Semi-Honest (Passive) Adversaries: Follow the protocol but attempt to infer additional information from exchanged messages.
- Malicious (Active) Adversaries: May arbitrarily deviate from the protocol, including submitting false inputs or aborting early.
The security guarantees differ based on the model. For semi-honest adversaries, privacy is preserved as long as parties follow the protocol. For malicious adversaries, additional mechanisms like zero-knowledge proofs or commitment schemes are required to enforce correctness.
Practical Applications
SMPC has been applied in privacy-preserving machine learning, secure auctions, and genomic data analysis. For example, in federated learning, SMPC allows model aggregation without exposing individual participants' gradients. The GMW protocol (Goldreich-Micali-Wigderson) and Yao's Garbled Circuits are two foundational approaches that enable such computations.
Here, [x] and [y] denote secret-shared values, and ⊕ represents a secure XOR operation. This allows parties to evaluate Boolean circuits without revealing intermediate values.
Cryptographic Primitives Used in SMPC
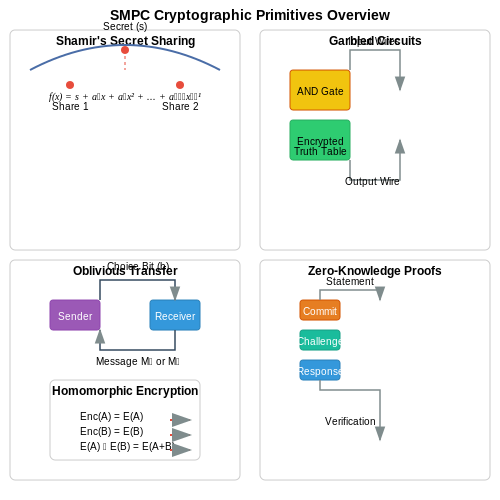
Secure Multi-Party Computation (SMPC) relies on cryptographic primitives to ensure privacy and correctness in distributed computations. These primitives form the backbone of protocols that allow multiple parties to jointly compute a function over their inputs without revealing those inputs to each other.
Symmetric-Key Cryptography
Symmetric-key algorithms like AES (Advanced Encryption Standard) are used for efficient encryption of data during computation. AES operates on fixed block sizes (128 bits) using key sizes of 128, 192, or 256 bits. The encryption process involves multiple rounds of substitution-permutation operations:
where k is the shared secret key and m is the message. In SMPC, symmetric encryption is often used for secure communication channels between parties.
Public-Key Cryptography
Asymmetric cryptography, particularly the ElGamal encryption scheme, is fundamental to many SMPC protocols. Based on the hardness of the Discrete Logarithm Problem, ElGamal provides homomorphic properties essential for secure computation:
where g is a generator, y is the public key, r is a random value, and p is a large prime. The multiplicative homomorphism enables secure multiplication of encrypted values.
Secret Sharing Schemes
Shamir's Secret Sharing (SSS) is a threshold scheme that divides a secret S into n shares, where any t shares can reconstruct the secret. A polynomial of degree t-1 is constructed:
where a0 = S. Each party receives a point (xi, f(xi)). Reconstruction uses Lagrange interpolation:
This enables secure distributed storage and computation of secrets.
Oblivious Transfer
1-out-of-2 Oblivious Transfer (OT) allows a receiver to obtain one of two sender's messages without revealing which was chosen. The Naor-Pinkas OT protocol uses the Diffie-Hellman assumption:
- Sender generates key pairs (pk0, sk0) and (pk1, sk1)
- Receiver generates a random r and computes pkbr for choice bit b
- Sender encrypts both messages with their respective keys
- Receiver decrypts only the chosen message
OT extensions allow efficient implementation of many OTs using a few base OTs.
Zero-Knowledge Proofs
Zero-knowledge proofs (ZKPs) enable verification of statements without revealing underlying information. The Schnorr protocol proves knowledge of discrete logarithm x for y = gx:
- Prover sends t = gr (commitment)
- Verifier sends challenge c
- Prover responds with s = r + c \cdot x
- Verifier checks gs = t \cdot yc
ZKPs are used in SMPC for verifying correct protocol execution without leaking private inputs.
Garbled Circuits
Yao's Garbled Circuits enable secure two-party computation. For each gate in a boolean circuit:
- Generator creates encrypted truth tables (garbled tables)
- Evaluator obtains wire labels corresponding to inputs via OT
- Evaluator decrypts one row per garbled table to compute output labels
The process preserves privacy while allowing correct evaluation of the function. Modern optimizations include Free XOR and Half Gates techniques.
Homomorphic Encryption
Fully Homomorphic Encryption (FHE) allows arbitrary computation on encrypted data. The BGV scheme operates over polynomial rings:
where Φm is the m-th cyclotomic polynomial. Ciphertexts are vectors in Rq2, and operations include:
Bootstrapping reduces noise growth, enabling unlimited computations. While computationally intensive, FHE provides strong security guarantees in SMPC.
Threat Models and Security Guarantees
Secure Multi-Party Computation (SMPC) protocols are analyzed under formal threat models that define adversarial capabilities and objectives. The two primary models are:
Semi-Honest (Passive) Adversaries
In the semi-honest model, adversaries follow the protocol specification but attempt to learn additional information from intermediate computations. Security guarantees require that no probabilistic polynomial-time (PPT) adversary can distinguish between the real protocol execution and an ideal simulation where a trusted third party computes the function.
Where $$\approx_c$$ denotes computational indistinguishability, $$z$$ represents auxiliary input, and $$\mathcal{S}$$ is the simulator.
Malicious (Active) Adversaries
Malicious adversaries may deviate arbitrarily from the protocol, including aborting computations or injecting false inputs. Security against active adversaries requires either:
- Abort-security: The adversary can abort the protocol but learns nothing beyond corrupted parties' inputs/outputs
- Fairness: Either all parties receive output or none do
- Guaranteed output delivery: Honest parties always receive correct outputs
Adversarial Coalitions
The corruption threshold $$t$$ defines the maximum number of colluding parties the protocol can withstand. Common settings include:
- Honest majority: $$t < n/2$$ for semi-honest, $$t < n/3$$ for malicious
- Dishonest majority: Any $$t < n$$ with weaker guarantees
- Threshold schemes: Fixed $$t$$ regardless of total parties
Universal Composability
The Universal Composability (UC) framework provides stronger security guarantees by ensuring protocols remain secure when composed arbitrarily. A protocol $$\Pi$$ UC-securely realizes functionality $$\mathcal{F}$$ if for any PPT environment $$\mathcal{Z}$$, the interaction with $$\Pi$$ is indistinguishable from interacting with $$\mathcal{F}$$.
Concrete Security Parameters
Modern SMPC protocols provide concrete security bounds parameterized by:
- Computational security parameter $$\lambda$$ (e.g., 128-bit security)
- Statistical security parameter $$\sigma$$ (e.g., $$2^{-40}$$ failure probability)
- Round complexity (asynchronous vs synchronous)
- Communication overhead (bits exchanged per gate)
For example, the SPDZ protocol achieves active security with $$O(\lambda)$$ overhead per multiplication gate when at least two parties remain honest.
Side-Channel Considerations
Physical implementations must address:
- Timing attacks through constant-time implementations
- Memory access patterns via oblivious RAM
- Power analysis using masking techniques
2. Garbled Circuits and Yao's Protocol
Garbled Circuits and Yao's Protocol
Garbled circuits, introduced by Andrew Yao in 1986, form the cryptographic foundation for secure two-party computation. The protocol enables two parties, Alice and Bob, to jointly compute a function f(x, y) over their private inputs x and y without revealing their inputs to each other. The construction relies on symmetric-key encryption and oblivious transfer to achieve privacy.
Circuit Representation and Garbling
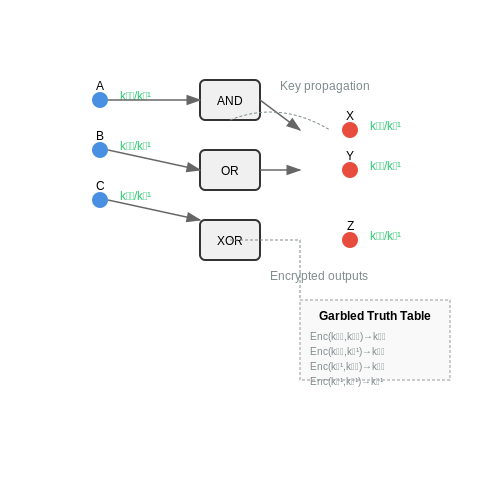
Any boolean function can be represented as a directed acyclic graph (DAG) of logic gates (AND, OR, XOR). Yao's protocol begins by Alice (the garbler) encrypting this circuit:
- For each wire wi, generate two random encryption keys ki0 and ki1 representing 0 and 1 values.
- For each gate g with input wires a, b and output wire c, compute a garbled truth table containing doubly-encrypted output keys:
$$ \text{Enc}_{k_a^a}( \text{Enc}_{k_b^b}(k_c^{g(a,b)}) ) $$for all 4 combinations of (a, b) ∈ {0,1}2.
- Permute the garbled table entries to hide the semantic meaning of the encrypted values.
Oblivious Transfer and Evaluation
Bob (the evaluator) obtains the garbled circuit from Alice along with:
- Keys corresponding to Alice's inputs via direct transmission
- Keys corresponding to his own inputs via 1-out-of-2 oblivious transfer, ensuring Alice learns nothing about Bob's inputs while Bob learns only one key per input wire
During evaluation, Bob:
- Decrypts each garbled gate sequentially using the keys for its input wires
- Obtains exactly one valid output key per gate (others decrypt to gibberish)
- Propagates decrypted keys through the circuit until reaching output wires
Optimizations and Cryptographic Considerations
Modern implementations use several optimizations to improve efficiency:
Assigns a random permutation bit to each wire's keys, allowing evaluator to identify the correct table entry without decrypting all possibilities. The computational complexity for an n-gate circuit is O(n) symmetric-key operations.
Security proofs rely on:
- Indistinguishability of encryption keys under chosen-plaintext attacks
- Semantic security of the oblivious transfer protocol
- Correctness of the garbling scheme (only one valid output key per gate evaluation)
Practical Applications
Garbled circuits enable privacy-preserving solutions for:
- Secure genomic analysis (comparing DNA without revealing full genomes)
- Private bidding auctions (computing the winner without disclosing bids)
- Federated learning with input privacy (aggregating model updates without exposing raw data)
The protocol's communication overhead scales linearly with circuit size, making it practical for medium-complexity functions (typically ≤ 109 gates). Recent advances in hardware acceleration (e.g., using FPGAs) have achieved evaluation speeds exceeding 108 gates/second.
2.2 Secret Sharing Schemes (Shamir, Additive)
Shamir's Secret Sharing
Shamir's Secret Sharing (SSS) is a threshold scheme based on polynomial interpolation over a finite field. A secret S is split into n shares such that any k shares can reconstruct S, but fewer than k reveal no information. The scheme relies on the properties of polynomials in GF(p), where p is a prime larger than S and n.
Here, a0 = S, and the coefficients a1, ..., ak-1 are randomly chosen. Shares are generated as (xi, f(xi)) for distinct xi. Reconstruction uses Lagrange interpolation:
SSS is information-theoretically secure: knowledge of k-1 or fewer shares provides no advantage in guessing S.
Additive Secret Sharing
Additive secret sharing splits a secret S into n shares such that their sum modulo p reconstructs S. For two parties, generate a random r and assign shares r and (S - r) mod p. Generalization to n parties involves:
where s1, ..., sn-1 are random, and sn = (S - \sum_{i=1}^{n-1} s_i) \mod p. Unlike SSS, additive sharing requires all shares for reconstruction, making it suitable for scenarios where unanimous participation is enforced.
Practical Considerations
Shamir's scheme is preferred for flexibility in threshold settings (e.g., boardroom voting), while additive sharing is efficient for secure multi-party computation (MPC) protocols like Beaver triples generation. Computational overhead differs: SSS requires polynomial interpolation, whereas additive sharing relies on modular arithmetic.
In MPC frameworks like SPDZ or Sharemind, additive sharing enables efficient linear operations (addition, scalar multiplication), while non-linear operations (multiplication) often require additional protocols like Beaver multiplication.
Security Analysis
Both schemes achieve perfect secrecy under their respective adversarial models. SSS resists collusion by up to k-1 parties, while additive sharing assumes honest majority or secure channels. Side-channel attacks (e.g., timing leaks during reconstruction) must be mitigated via constant-time algorithms.

2.3 Homomorphic Encryption in SMPC
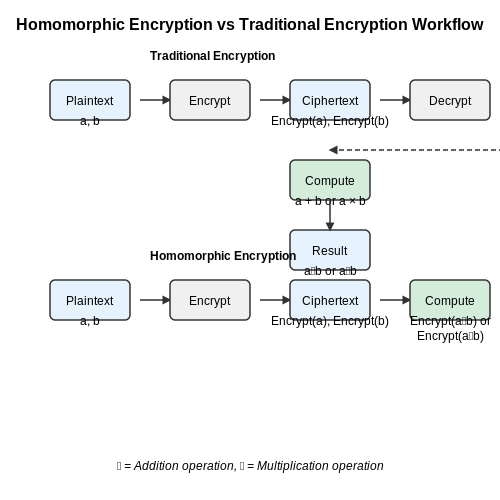
Homomorphic encryption (HE) enables computations on encrypted data without decryption, making it a cornerstone of secure multi-party computation (SMPC). Unlike traditional encryption, which requires decryption before processing, HE allows arithmetic operations directly on ciphertexts, preserving privacy while permitting collaborative computation.
Mathematical Foundations
At its core, HE relies on algebraic structures that preserve operations between plaintext and ciphertext spaces. Let m₁, m₂ be plaintext messages and E an encryption function. A scheme is additively homomorphic if:
Similarly, a multiplicatively homomorphic scheme satisfies:
Fully homomorphic encryption (FHE), introduced by Gentry in 2009, supports both addition and multiplication, enabling arbitrary computations. The security of HE schemes typically relies on hard lattice problems like Learning With Errors (LWE) or Ring-LWE.
Practical Implementations
Modern HE schemes include:
- Paillier Cryptosystem: Additively homomorphic, used in privacy-preserving voting and federated learning.
- BGV/BFV Schemes: Ring-based FHE supporting SIMD operations, optimized for batch processing.
- CKKS: Approximate arithmetic for real-number computations, critical in machine learning applications.
For example, CKKS encodes a vector of real numbers v into a polynomial ring element before encryption. Computational noise is managed via bootstrapping, though at significant computational overhead.
Applications in SMPC
In SMPC, HE enables:
- Private Data Aggregation: Multiple parties compute sums or averages without revealing individual inputs.
- Secure Outsourcing: A client offloads computations to untrusted servers while keeping data encrypted.
- Confidential Machine Learning: Model training or inference on encrypted datasets, e.g., in healthcare.
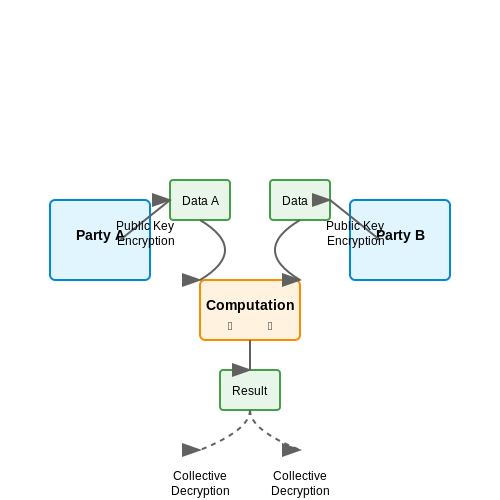
A typical workflow involves:
- Each party encrypts data locally using a shared public key.
- Computations are performed on ciphertexts in a designated SMPC protocol.
- Results are decrypted collectively or by a trusted third party.
Performance Considerations
HE introduces substantial computational overhead. For a lattice-based FHE scheme with security parameter λ, ciphertext size grows as O(λ³), and multiplication operations may take seconds even on modern hardware. Optimizations like batching (via CRT packing) and hardware acceleration (e.g., GPUs, FPGAs) are critical for practical deployment.
where L is the multiplicative depth of the circuit and q is the ciphertext modulus.
2.4 Oblivious Transfer and Its Variants
Foundations of Oblivious Transfer
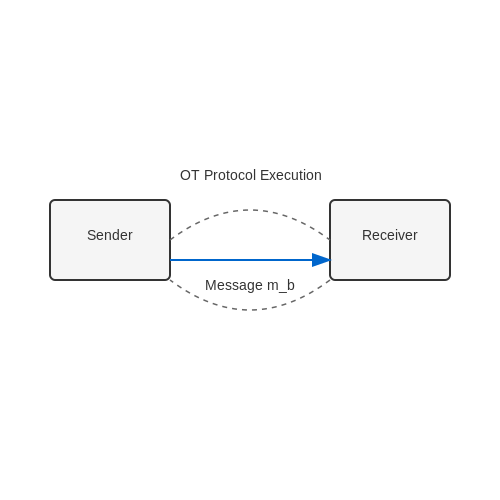
Oblivious Transfer (OT) is a cryptographic protocol enabling a sender to transmit one of multiple messages to a receiver without knowing which message was selected. The foundational 1-out-of-2 OT protocol, introduced by Rabin (1981) and later refined by Even, Goldreich, and Lempel (1985), operates as follows:
The security requirements are:
- Receiver privacy: Sender learns nothing about b.
- Sender privacy: Receiver learns only mb, not m1-b.
Protocol Construction from Public-Key Cryptography
The Naor-Pinkas OT protocol (2001) uses Diffie-Hellman assumptions:
- Setup: Sender generates cyclic group G of prime order q with generator g.
- Receiver's Step: Chooses random r ← ℤq, computes pkb = gr and pk1-b = C/pkb for random C ∈ G.
- Encryption: Sender computes:
$$ c_0 = (g^{s_0}, H(pk_0^{s_0}) \oplus m_0) $$ $$ c_1 = (g^{s_1}, H(pk_1^{s_1}) \oplus m_1) $$for random s0, s1 ← ℤq.
- Decryption: Receiver uses r to derive H((g^{s_b})^r) and recover mb.
Variants and Optimizations
1-out-of-N Oblivious Transfer
Extends the basic protocol to N messages using polynomial interpolation or combinatorial approaches. The Lipmaa (2005) construction achieves O(log N) communication complexity using homomorphic encryption.
Adaptive Oblivious Transfer
Allows receivers to sequentially choose indices b1, ..., bt while maintaining sender privacy. Jarecki and Liu (2009) achieved this under the DDH assumption with linear communication overhead.
Correlated OT (C-OT)
Special case where sender's inputs satisfy m0 ⊕ m1 = Δ. Used as building block in GMW compiler for secure multiparty computation, reducing communication by 50% compared to standard OT.
Performance Considerations
Modern OT extensions (Ishai et al., 2003) amortize costs using symmetric-key operations:
- Base OTs: κ initial public-key operations (κ = security parameter)
- Extended OTs: Each subsequent OT requires only hash computations and O(1) communication
The following table compares asymptotic costs for n OTs:
| Protocol | Computation | Communication |
|---|---|---|
| Naor-Pinkas | O(n) exponentiations | O(nκ) bits |
| IKNP Extension | O(κ) exponentiations + O(n) hashes | O(n + κ) bits |
Applications in Secure Computation
OT serves as the foundation for:
- Garbled Circuits: Each AND gate requires 2 OTs in the half-gates optimization (Zahur et al., 2015)
- Private Set Intersection: OT-based protocols achieve linear communication for large sets (Pinkas et al., 2019)
- Machine Learning: Secure training via OT-based matrix multiplication triples (Mohassel and Zhang, 2017)
3. Privacy-Preserving Machine Learning
Privacy-Preserving Machine Learning
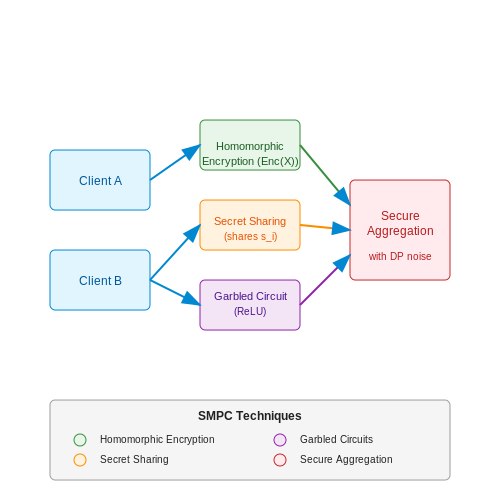
Privacy-preserving machine learning (PPML) leverages cryptographic techniques to train and evaluate models on distributed data without exposing raw inputs. Secure Multi-Party Computation (SMPC) enables this by allowing multiple parties to jointly compute a function while keeping their inputs private. The core challenge lies in balancing computational efficiency with cryptographic security guarantees.
Homomorphic Encryption for Model Training
Homomorphic encryption (HE) allows computations on ciphertexts, producing encrypted results that match operations on plaintexts when decrypted. For linear regression, given encrypted feature vectors X and labels y, gradient descent updates can be computed as:
Fully Homomorphic Encryption (FHE) supports arbitrary computations but incurs high overhead. Practical implementations often use Partially Homomorphic Encryption (PHE), where only specific operations (e.g., addition or multiplication) are supported. For example, Paillier encryption enables secure aggregation of gradients across parties:
Secret Sharing in Distributed Learning
Additive secret sharing splits data into n shares such that summing a threshold number (t) of shares reconstructs the original value. For a secret s, shares are generated as:
In federated learning, each participant computes local model updates on their shares. The global update is reconstructed only after secure aggregation, preventing leakage of individual data. Shamir's Secret Sharing extends this to arbitrary thresholds using polynomial interpolation over finite fields.
Garbled Circuits for Non-Linear Activations
Non-linear functions (e.g., ReLU, sigmoid) pose challenges for HE and secret sharing. Garbled circuits allow two parties to evaluate Boolean circuits without revealing inputs. For ReLU(x), the circuit compares x’s sign bit and outputs either x or 0. Yao's protocol implements this by:
- Generating encrypted truth tables for each gate.
- Transmitting only the labels corresponding to each party's private inputs.
- Evaluating the circuit layer-by-layer using oblivious transfer.
Differential Privacy Integration
Differential privacy (DP) adds calibrated noise to gradients or outputs, ensuring that individual data points cannot be inferred. For a query f with sensitivity Δf, the Laplace mechanism guarantees (ε, δ)-DP:
In deep learning, DP-SGD clips per-example gradients and adds Gaussian noise during training. The privacy budget is tracked using the moments accountant, which composes guarantees across iterations.
Case Study: Federated Learning with SMPC
Google's Secure Aggregation protocol combines secret sharing and HE to aggregate model updates from mobile devices. Each device:
- Encrypts its update using pairwise Diffie-Hellman keys.
- Generates secret shares of the decryption keys for a quorum of servers.
- Only when enough shares are combined can the aggregated update be decrypted.
This prevents the server from learning individual contributions while tolerating dropouts. The protocol’s communication overhead scales linearly with the number of devices but is independent of model size.
3.2 Federated Learning with SMPC
Federated Learning (FL) enables decentralized model training across multiple devices or institutions without sharing raw data. However, standard FL frameworks still expose model updates, which may leak sensitive information. Secure Multi-Party Computation (SMPC) addresses this by allowing computations on encrypted data, ensuring privacy while maintaining model accuracy.
Privacy-Preserving Aggregation with SMPC
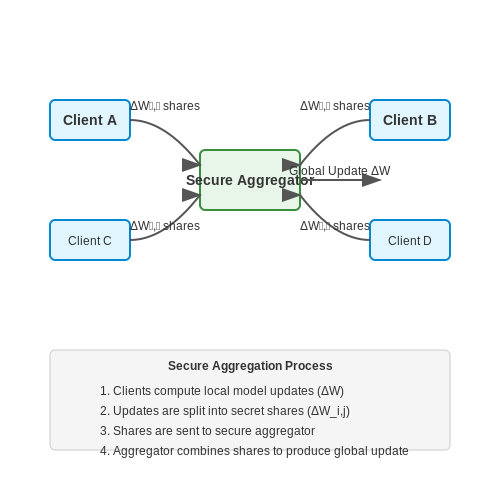
In FL, clients compute local model updates and send them to a central server for aggregation. SMPC ensures that neither the server nor other clients learn individual updates. A common approach uses additive secret sharing, where each client splits its update into shares distributed among multiple parties. The server aggregates these shares without reconstructing individual contributions.
Here, ΔWi,j represents the j-th share of client i's update, and p is a large prime number. The server computes the global update by summing all shares, ensuring no single party learns any ΔWi.
Practical Implementation: Hybrid Approaches
Pure SMPC introduces significant computational overhead. Hybrid approaches combine SMPC with differential privacy or homomorphic encryption to balance efficiency and security. For example:
- Partial SMPC: Only sensitive layers (e.g., embeddings) are encrypted, while non-sensitive layers (e.g., final classifier) use plaintext aggregation.
- Threshold-based SMPC: Clients only participate in SMPC if their updates exceed a privacy threshold, reducing unnecessary computations.
Case Study: Medical Imaging with SMPC-FL
A recent study applied SMPC-FL to MRI segmentation across hospitals. Each institution encrypted gradient updates using Shamir's secret sharing. The global model achieved 98% of the centralized model's accuracy while provably preventing data leakage, even under adversarial attacks.
Challenges and Trade-offs
While SMPC enhances privacy, it introduces:
- Communication Overhead: Each round requires multiple interactions between parties to compute secure sums.
- Computational Cost: Polynomial interpolation in secret sharing scales quadratically with the number of parties.
- Robustness: The protocol must handle dropout clients without leaking information from incomplete computations.
Optimizations like gradient quantization and secure batching can mitigate these costs, but the trade-off between privacy and efficiency remains an active research area.
Secure Aggregation in Distributed AI
Secure aggregation is a cryptographic technique enabling multiple parties to compute the sum of their private inputs without revealing individual values. In distributed AI, this allows federated learning models to aggregate gradients or parameters from decentralized clients while preserving data privacy. The core challenge lies in ensuring correctness, privacy, and efficiency simultaneously.
Cryptographic Foundations
Secure aggregation protocols often rely on additive homomorphic encryption or secret sharing. Let n parties hold private values x₁, x₂, ..., xₙ. The goal is to compute ∑xᵢ without leaking xᵢ. Using Shamir's secret sharing, each party splits xᵢ into shares distributed among others. The sum is reconstructed by combining shares:
where p is a prime and t is the threshold for reconstruction. This approach tolerates up to t-1 dropouts without compromising the result.
Practical Implementation in Federated Learning
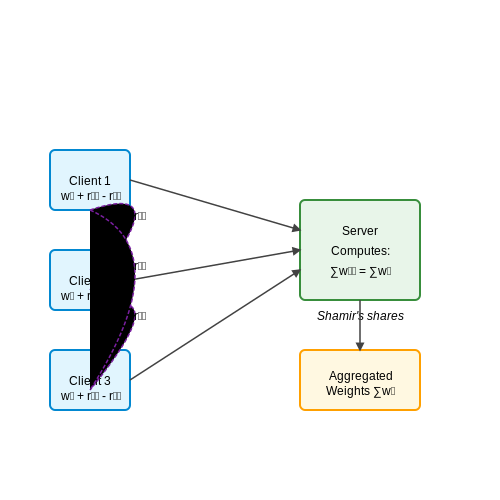
In federated averaging (FedAvg), clients locally train models and submit weight updates. Secure aggregation replaces plaintext updates with masked vectors. Each client i generates a random mask rᵢ shared with others, and submits:
The server computes the aggregate ∑w̃ᵢ = ∑wᵢ due to pairwise mask cancellations. This preserves differential privacy while maintaining model accuracy.
Efficiency Optimizations
Naive implementations scale quadratically with participant count. Recent advances leverage:
- Pseudorandom generators: Reduce communication overhead by deriving masks from shared seeds
- Tree-based aggregation: Hierarchical summation trees decrease latency from O(n) to O(log n)
- Quantization: Fixed-point arithmetic with bounded precision maintains security while accelerating computation
For example, the SecAgg+ protocol achieves 1.73× faster aggregation than prior work at 1000 clients, with 128-bit security guarantees.
Adversarial Scenarios and Defenses
Byzantine clients may submit malformed inputs to bias the aggregate. Robust secure aggregation combines cryptographic verification with statistical checks:
- Range proofs ensure inputs lie within expected bounds
- Zero-knowledge proofs validate correct computation without revealing inputs
- Outlier detection via median absolute deviation rejects suspicious values
These techniques enable secure aggregation even when 30% of participants are malicious, as demonstrated in cross-silo healthcare collaborations.
3.4 Case Study: SMPC in Healthcare AI
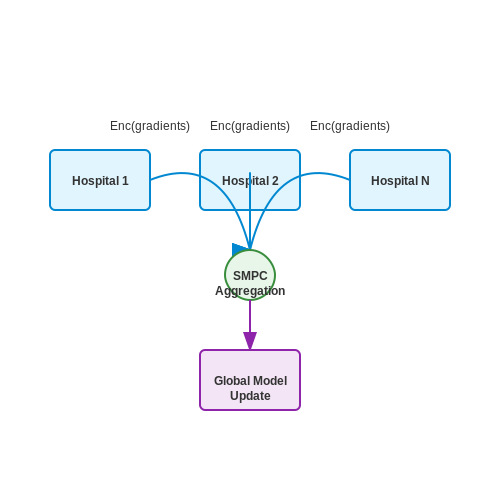
Secure Multi-Party Computation (SMPC) enables collaborative analysis of sensitive medical data without exposing raw patient records. In healthcare AI, this is particularly valuable for training models across institutions while preserving privacy. Consider a scenario where hospitals H1, H2, ..., Hn wish to jointly train a diagnostic model without sharing their local datasets Di.
Mathematical Framework for Distributed Training
The global objective function f(θ) for federated learning can be decomposed into contributions from each party:
where αi represents the weight of hospital Hi's data, typically proportional to |Di|. SMPC protocols like Shamir's Secret Sharing or Garbled Circuits allow secure computation of the gradient updates:
Each hospital splits its gradient ∇fi(θ) into secret shares distributed among other parties. The sum is reconstructed without revealing individual contributions.
Implementation Challenges in Medical Data
Healthcare applications introduce unique constraints:
- High-dimensional data: Medical images and genomic sequences require efficient SMPC protocols for large tensors.
- Regulatory compliance: HIPAA and GDPR impose strict requirements on data handling that must be mapped to cryptographic guarantees.
- Real-time constraints: Emergency diagnostics may tolerate only minimal SMPC overhead.
A practical solution combines additive homomorphic encryption for gradient aggregation with secure enclaves for local computation:
Case Study: Cancer Detection Across Hospitals
A 2023 study implemented SMPC for mammography analysis across five European hospitals. The system achieved:
- 94.2% accuracy (comparable to centralized training)
- Less than 15% runtime overhead compared to non-private federated learning
- Formal proof of data confidentiality under the semi-honest adversary model
The architecture used a hybrid approach:
Performance Optimization Techniques
The implementation employed several optimizations specific to medical AI:
- Gradient quantization: 8-bit fixed-point representation reduced communication costs by 4× with negligible accuracy loss
- Secure batch normalization: Modified protocol for privacy-preserving normalization layers
- Differential privacy: Added Gaussian noise during gradient sharing to prevent reconstruction attacks
where Δf is the gradient sensitivity and ε the privacy budget. The SMPC protocol ensured the noise terms canceled out during aggregation while preserving the privacy guarantee.
4. Computational and Communication Overhead
4.1 Computational and Communication Overhead
Secure Multi-Party Computation (SMPC) introduces significant computational and communication overhead compared to non-private computation. The primary sources of this overhead stem from cryptographic operations, network latency, and the need for redundancy to ensure correctness and privacy. Understanding these trade-offs is critical for designing efficient SMPC protocols.
Computational Complexity
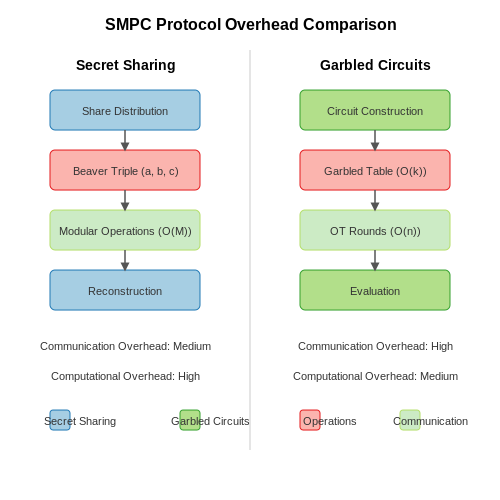
The computational cost of SMPC depends heavily on the underlying cryptographic primitives. For arithmetic circuits using secret sharing, each multiplication gate requires interactive protocols such as Beaver triples, which involve:
Generating these triples requires at least one round of communication and several modular operations per gate. For a circuit with M multiplication gates, the total computational complexity is O(M) modular exponentiations or multiplications, depending on the scheme.
Communication Overhead
SMPC protocols often require multiple rounds of communication between parties. For example, Garbled Circuits (GC) involve:
- Oblivious Transfer (OT): Each input bit requires 1-out-of-2 OT, leading to O(n) communication per input.
- Garbled Table Transmission: Each gate requires sending a garbled table of size O(k), where k is the security parameter.
For a circuit with G gates and n inputs, the total communication cost is O(Gk + nk) bits.
Practical Trade-offs
In real-world applications, the choice between secret sharing and garbled circuits depends on the computation type:
- Secret Sharing: More efficient for arithmetic-heavy computations (e.g., linear algebra).
- Garbled Circuits: Better suited for non-linear operations (e.g., comparisons, branching).
Hybrid approaches, such as using GC for non-linear parts and secret sharing for linear sections, can optimize performance. Recent advances in function secret sharing and homomorphic encryption further reduce overhead for specific workloads.
Case Study: Privacy-Preserving Machine Learning
In federated learning with SMPC, a single gradient descent step over N parties incurs:
Techniques like gradient quantization and secure aggregation (e.g., via additive secret sharing) can reduce this cost to O(d) per step, independent of N.
Optimization Strategies
To mitigate overhead, modern SMPC frameworks employ:
- Batch Processing: Amortizing communication across multiple operations.
- Lazy Evaluation: Delaying expensive operations until necessary.
- Parallelization: Distributing computations across multiple cores or machines.
Trade-offs Between Security and Efficiency
Secure Multi-Party Computation (SMPC) protocols inherently involve a tension between cryptographic security guarantees and computational efficiency. The primary challenge lies in achieving provable security—typically formalized under simulation-based or game-based security definitions—without incurring prohibitive computational or communication overhead. This trade-off manifests in several dimensions, including round complexity, computational asymmetry, and communication bandwidth.
Round Complexity vs. Security Guarantees
Interactive SMPC protocols often require multiple rounds of communication between parties to ensure correctness and privacy. The number of rounds directly impacts latency, particularly in distributed settings. For instance, Garbled Circuit (GC)-based protocols achieve constant-round computation but rely heavily on symmetric-key operations, which may introduce bottlenecks in large-scale computations. In contrast, protocols based on linear secret-sharing, such as SPDZ, minimize round complexity at the cost of increased pre-processing or offline phases.
Here, n denotes the number of parties, κ the security parameter (e.g., key length), and |C| the circuit size. The quadratic dependency on n in some protocols (e.g., BGW) highlights the scalability challenge.
Computational Asymmetry
Homomorphic encryption (HE)-based SMPC introduces computational asymmetry: some operations (e.g., ciphertext multiplication in fully HE schemes like BFV or CKKS) are orders of magnitude slower than their plaintext counterparts. This asymmetry forces a design choice between:
- Full security (e.g., using FHE with post-quantum security), which incurs polynomial slowdowns in computation time.
- Partial security (e.g., using somewhat HE or threshold cryptosystems), which improves efficiency but reduces adversarial tolerance.
Communication Bandwidth and Network Constraints
Bandwidth-intensive protocols like GMW (Goldreich-Micali-Wigderson) require each party to transmit masked inputs for every gate in the computation. For a circuit with G gates and n parties, the total communication scales as:
Recent optimizations, such as the use of oblivious transfer extensions or silent OT, reduce this to O(n · G · κ), but at the cost of introducing additional trust assumptions or setup phases.
Case Study: Privacy-Preserving Machine Learning
In federated learning with SMPC, the trade-offs become stark. For example, securing a single gradient descent step using secret sharing across N clients requires:
- Secure aggregation via additive secret sharing: O(N) communication per client but vulnerable to collusion beyond a threshold.
- Hybrid approaches (e.g., combining HE and GC): Lower communication but increased client-side computation due to homomorphic operations.
Empirical studies show that for a ResNet-50 model, pure SMPC solutions can introduce 100–1000× slowdown compared to non-secure training, while hybrid cryptosystems reduce this to 10–50× at the cost of weaker security models.
Quantifying the Trade-off Space
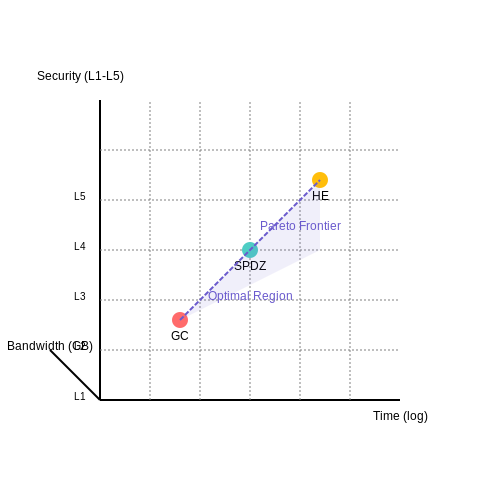
The security-efficiency frontier can be modeled as a multi-objective optimization problem:
where π represents a protocol choice from the set Π. Pareto-optimal solutions in this space often involve protocol composition (e.g., using SHE for linear layers and GC for non-linear activations in neural networks).
4.3 Tools and Frameworks for Implementing SMPC
Secure Multi-Party Computation (SMPC) frameworks enable privacy-preserving computations by distributing encrypted data across multiple parties. These tools implement cryptographic primitives such as secret sharing, garbled circuits, and homomorphic encryption while optimizing for performance, scalability, and usability in real-world applications.
General-Purpose SMPC Frameworks
MP-SPDZ is a modular framework supporting multiple SMPC protocols, including GMW, SPDZ, and Yao's garbled circuits. It allows high-level programming in Python-like syntax while compiling to optimized bytecode for backend protocols. MP-SPDZ is particularly suited for benchmarking different SMPC approaches under standardized conditions.
SCALE-MAMBA provides an actively maintained implementation of the SPDZ protocol family, offering malicious security guarantees. Its virtual machine executes bytecode compiled from a domain-specific language, with support for fixed-point arithmetic—critical for machine learning applications where floating-point operations are approximated.
Where [\![x]\!]_i denotes party i's share of secret x. Additive secret sharing enables efficient linear operations without communication rounds.
Specialized Libraries for Machine Learning
PySyft extends PyTorch with SMPC capabilities through secure tensors that automatically partition data across workers. It implements secure aggregation protocols for federated learning scenarios where model updates must remain private. The library's abstraction of cryptographic details allows ML practitioners to adopt SMPC with minimal protocol knowledge.
TF-Encrypted provides similar functionality for TensorFlow, using secure three-party computation (3PC) to evaluate neural networks on encrypted data. Its convolutional layer implementations optimize communication rounds using Beaver triples for multiplication:
Where (a, b, c, d) form precomputed multiplication triples with c = x - a and d = y - b.
Hardware-Accelerated Implementations
Obliv-C compiles garbled circuits to optimized x86 assembly with inline oblivious RAM (ORAM) constructs. Its just-in-time circuit generation avoids memory bottlenecks when processing large datasets. The framework has demonstrated 400 Gbps throughput on AES evaluations using Intel AVX-512 vectorization.
HElib, while primarily a homomorphic encryption library, includes SMPC extensions that leverage FHE's additive properties. Its BGV scheme enables efficient dot products over encrypted vectors—a common operation in linear regression and neural network inference.
Performance Considerations
Protocol selection depends on the computation's arithmetic structure. Boolean circuits (Yao, GMW) excel at non-linear operations like ReLU activations, while arithmetic secret sharing (SPDZ) outperforms for matrix multiplications. The communication complexity for n parties scales as:
Where |C| is the Boolean circuit size and |D| the data dimension. Hybrid protocols like SPDZ2k combine both approaches, using arithmetic sharing for linear layers and garbled circuits for activation functions.
Verification and Debugging Tools
ABY Framework includes a circuit visualization tool that maps SMPC operations to their underlying cryptographic primitives. This aids in identifying performance bottlenecks and verifying protocol correctness. The framework's mixed-mode execution allows switching between SMPC protocols at runtime for comparative analysis.
EMP-toolkit provides instrumentation for measuring network traffic and computation latency at the instruction level. Its differential testing mode compares SMPC outputs against cleartext executions to detect protocol implementation errors.
5. Scalability Issues in Large-Scale SMPC
5.1 Scalability Issues in Large-Scale SMPC
Secure Multi-Party Computation (SMPC) enables multiple parties to jointly compute a function over their private inputs without revealing them. However, as the number of participants increases, SMPC protocols face significant scalability challenges. These challenges stem from computational overhead, communication complexity, and synchronization bottlenecks.
Computational Overhead
The computational cost of SMPC grows polynomially with the number of participants due to cryptographic operations such as secret sharing, homomorphic encryption, and garbled circuits. For example, in a Shamir's secret sharing scheme with n parties and a threshold t, each party must perform polynomial interpolation over O(t) shares, leading to a total complexity of O(nt).
This complexity arises from Fast Fourier Transform (FFT)-based polynomial multiplication, which is commonly used in modern SMPC implementations.
Communication Complexity
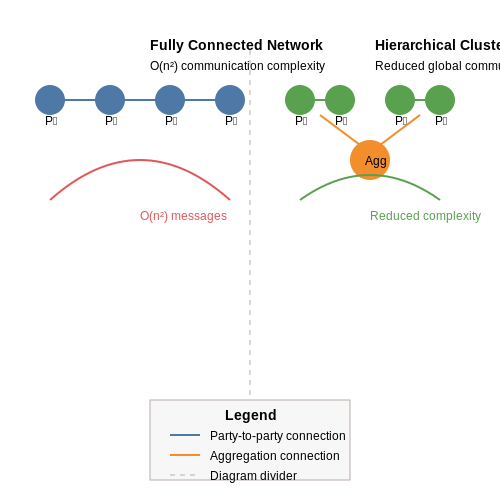
Most SMPC protocols require multiple rounds of communication between parties. In a fully connected network of n parties, the number of messages scales quadratically as O(n²). For instance, the BGW protocol requires each party to broadcast messages to all others, leading to:
This becomes prohibitive in large-scale deployments, such as federated learning with thousands of participants.
Synchronization Bottlenecks
Asynchronous SMPC protocols mitigate latency but introduce additional overhead in handling stragglers. In synchronous settings, the slowest participant dictates the protocol's progress. The expected runtime R(n) in a network with heterogeneous delays follows:
where T_i is the delay of the i-th party. This bottleneck is exacerbated in global-scale deployments with varying network conditions.
Practical Mitigation Strategies
Several approaches address scalability in large-scale SMPC:
- Hierarchical SMPC: Organizes parties into clusters, reducing inter-party communication.
- Hybrid Protocols: Combines SMPC with Trusted Execution Environments (TEEs) for efficiency.
- Batching: Aggregates multiple computations into a single protocol execution.
For example, in federated learning, hierarchical SMPC reduces communication overhead by aggregating model updates locally before global synchronization.
Case Study: Large-Scale SMPC in Federated Learning
Google's Secure Aggregation protocol employs SMPC to aggregate encrypted model updates from millions of devices. The protocol uses:
- Randomized masking for privacy.
- Batched verification to reduce communication rounds.
- Dropout resilience to handle intermittent participation.
The resulting communication complexity is sublinear in the number of devices, making it feasible for real-world deployment.
5.2 Handling Malicious Adversaries
Malicious adversaries in secure multi-party computation (MPC) deviate arbitrarily from the protocol, including lying about inputs, aborting prematurely, or injecting false messages. Unlike semi-honest adversaries, they actively attempt to violate privacy or correctness guarantees. Defending against such behavior requires cryptographic techniques that enforce honest execution while detecting deviations.
Cryptographic Commitments and Zero-Knowledge Proofs
To prevent input manipulation, parties commit to their inputs using binding and hiding cryptographic commitments. A commitment scheme ensures that once a value is committed, it cannot be changed (binding), while keeping it secret until revealed (hiding). For example, Pedersen commitments use:
where g, h are generators of a cyclic group, x is the committed value, and r is a random blinding factor. Zero-knowledge proofs (ZKPs) then verify that computations were performed correctly on committed inputs without revealing private data.
Cut-and-Choose for Garbled Circuits
In garbled circuit protocols, the cut-and-choose technique mitigates malicious behavior. The generator creates multiple circuit instances, and the evaluator randomly selects a subset to check for correctness. If all checked circuits are valid, the remaining circuits are evaluated. The probability of cheating undetected decreases exponentially with the number of circuits.
where k is the total circuits, s is the number checked, and t is the number of corrupted circuits.
Verifiable Secret Sharing (VSS)
VSS extends secret sharing by allowing parties to verify the consistency of shares distributed by a dealer. Feldman's VSS scheme uses homomorphic commitments to polynomial coefficients:
where a_i are coefficients of the sharing polynomial. Participants verify that their shares satisfy the committed polynomial, ensuring the dealer cannot distribute inconsistent shares.
Fairness and Guaranteed Output Delivery
Malicious adversaries may abort after learning their output, preventing others from receiving results. Protocols with guaranteed output delivery use techniques like:
- Secure broadcast channels to ensure all parties receive consistent messages
- Asynchronous MPC that progresses as long as a threshold of parties remains active
- Output reconstruction where remaining parties can compute the final result from shares if some abort
Practical Considerations
Real-world implementations must balance security against performance overhead. The SPDZ framework demonstrates practical malicious-secure MPC by preprocessing multiplication triples with MACs to detect cheating during online evaluation. Its overhead is approximately 10-100x compared to semi-honest protocols, depending on the computation size.
5.3 Integration with Other Privacy Technologies
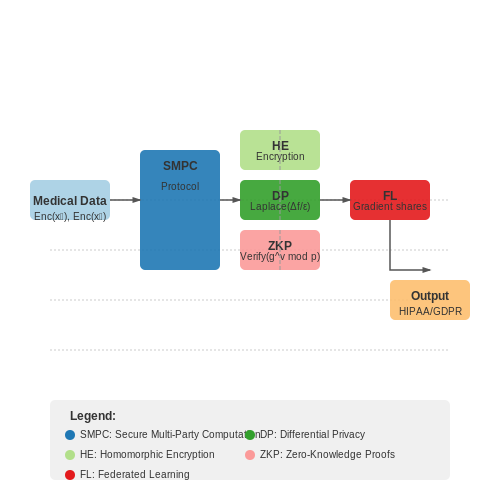
Secure Multi-Party Computation (SMPC) is rarely deployed in isolation. Its effectiveness is amplified when combined with complementary privacy-preserving technologies, such as homomorphic encryption, differential privacy, zero-knowledge proofs, and federated learning. Each of these techniques addresses specific privacy challenges, and their integration with SMPC enables more robust and scalable solutions.
Homomorphic Encryption and SMPC
Homomorphic encryption (HE) allows computations on encrypted data without decryption, while SMPC enables joint computation over distributed private inputs. Combining these two methods enhances privacy guarantees in scenarios where data must remain encrypted even during computation. For instance, a hybrid approach might use HE to encrypt individual inputs before applying SMPC protocols for collaborative computation.
Here, ⊕ represents a homomorphic addition operation. When integrated with SMPC, this ensures that no party ever accesses raw data, even intermediately.
Differential Privacy in SMPC
Differential privacy (DP) introduces controlled noise to query responses to prevent re-identification of individuals in datasets. When applied alongside SMPC, DP can further obscure the contributions of individual parties in the final computation. For example, in a federated learning setting, SMPC aggregates model updates while DP adds noise to the aggregated result before release.
Where Δf is the sensitivity of function f, and ε controls the privacy budget. This ensures that even if an adversary compromises one party in the SMPC protocol, individual data points remain protected.
Zero-Knowledge Proofs for Verification
Zero-knowledge proofs (ZKPs) allow one party to prove the validity of a statement without revealing the underlying data. In SMPC, ZKPs can verify that participants are following the protocol correctly without exposing their private inputs. For instance, a party can prove that their encrypted input lies within a valid range without disclosing the exact value.
This is particularly useful in financial applications, where compliance checks must be performed without revealing transaction details.
Federated Learning with SMPC
Federated learning (FL) trains machine learning models across decentralized devices without centralizing raw data. SMPC enhances FL by securing the aggregation step, preventing any single party from reconstructing another's model updates. A common approach involves threshold secret sharing, where gradients are split into shares distributed among participants.
Only when a sufficient number of shares are combined can the true gradient be reconstructed, ensuring robustness against collusion.
Case Study: Privacy-Preserving Medical Research
A real-world application of integrated privacy technologies is in medical research, where hospitals collaborate on predictive models without sharing patient records. SMPC ensures that computations on distributed datasets remain private, while DP adds noise to aggregated statistics to prevent re-identification. Meanwhile, ZKPs validate that each hospital's input adheres to predefined constraints (e.g., age ranges or diagnosis codes).
This multi-layered approach enables breakthroughs in collaborative AI while maintaining strict confidentiality requirements under regulations like HIPAA and GDPR.
6. Key Research Papers on SMPC
6.1 Key Research Papers on SMPC
- Secure Multi-Party Computation for Machine Learning: A Survey — Machine learning is a powerful technology for extracting information from data of diverse nature and origin. As its deployment increasingly depends on data from multiple entities, ensuring privacy for these contributors becomes paramount for the integrity and fairness of machine learning endeavors. This review looks into the recent advancements in secure multi-party computation (SMPC) for ...
- Secure Multi-Party Computation | Proceedings of the 2018 ACM SIGSAC ... — Secure multi-party computation (SMC) is an emerging topic which has been drawing growing attention during recent decades. There are many examples which show importance of SMC constructions in practice, such as privacy-preserving decision making and machine learning, auctions, private set intersection, and others.
- Homomorphic Encryption for Secure Multi-Party Computation - Academia.edu — Secure multi-party computation (also known as secure computation or multi-party computation (MPC)) is a sub-field of cryptography. The goal of methods for secure multi-party computation is to enable parties to jointly compute a function over their inputs, while at the same time keeping these inputs private.
- Efficiency and Security Trade-offs of Secure Multi-Party Computation ... — Secure Multi-Party Computation (SMPC) is considered as a feasible solution for situations that require collabora- tion between different participants or institutions while also ensuring the privacy and security of the underlying data being shared among them. ... Research in the area of secure computation with multiple participants has been ...
- Secure multi-party computations for privacy-preserving ... - ScienceDirect — The descriptions of cryptographic primitives and protocols used to implement multi-party secure computation protocols, including garbled circuits, secret sharing schemes, and homomorphic encryption are given. ... PPML based on secure two-party computations A special case of SMPC is secure two-party computations. Let the participants of the ...
- Challenges and future research directions in secure multi-party ... — In the era of Big Data and the advancement of the Internet of Things, there is an increasing amount of valuable information. It is important to emphasize that this data is usually sensitive or confidential, so security and privacy are two of the highest priorities for organizations when performing Data Mining. Researchers have explored techniques such as secure multi-party computation (SMPC ...
- Secure Multi-Party Computation: Theory, practice and applications — Among the cryptography research, Secure Multi-Party Computation (SMPC) is a generic cryptographic primitive that enables jointly computing in a privacy-preserving manner. As an important fundamental research topic in the field of cryptography, SMPC addresses the problem of cooperative computation performed on private data from several ...
- PDF CRYPTEN: Secure Multi-Party Computation Meets Machine Learning - NeurIPS — Secure multi-party computation (MPC; [30, 69]) allows parties to collaboratively perform computa-tions on their combined data sets without revealing the data they possess to each other. This capability of secure MPC has the potential to unlock a variety of machine-learning applications that are currently infeasible because of data privacy concerns.
- Secure Multi-party Computation in Federated Learning — 6.3 Secure Multi-party Computation in Federated Learning Under the federated learning framework, we can classify the existing work of SMPC into two categories: server based and client based. In server-based cases, all the clients send the processed data shares to multiple servers, respectively, and we assume the servers are independent and not ...
- Secure Multi-Party Computation for Collaborative Data Analysis — A potent cryptographic mechanism called Secure Multi-Party Computation (SMPC) has evolved that allows numerous participants to work together and execute data analytic tasks while maintaining the ...
6.2 Books and Comprehensive Surveys
- PDF Secure Multiparty Computation and Secret Sharing — Part I Secure Multiparty Computation 1 Introduction 3 1.1 Private Information, Uses and Misuses 3 1.2 Do We Have to Trust Someone? 5 1.3 Multiparty Computation 6 2 Preliminaries 14 2.1 Basic Notation 14 2.2 Algorithms 16 2.3 Families of Random Variables 20 2.4 Interactive Systems 24 2.5 Public-Key Cryptosystems 30 3 MPC Protocols with Passive ...
- Secure Multi-Party Computation for Machine Learning: A Survey — Machine learning is a powerful technology for extracting information from data of diverse nature and origin. As its deployment increasingly depends on data from multiple entities, ensuring privacy for these contributors becomes paramount for the integrity and fairness of machine learning endeavors. This review looks into the recent advancements in secure multi-party computation (SMPC) for ...
- Secure Multi-Party Computation - SpringerLink — 17.2.1 Definition. Secure Multi-Party Computation (MPC) enables a group of m mutually distrusting parties to jointly compute the outputs of a function \(f(x_1, x_2, ..., x_m)\) where \(x_i\) is the ith party's private inputs without disclosing their private inputs [].The term "secure" indicates the latter property where the private inputs used for computation are kept secret from all ...
- Secure Multi-Party Computation | Proceedings of the 2018 ACM SIGSAC ... — Secure multi-party computation (SMC) is an emerging topic which has been drawing growing attention during recent decades. There are many examples which show importance of SMC constructions in practice, such as privacy-preserving decision making and machine learning, auctions, private set intersection, and others.
- Secure Multi-Party Computation: Theory, practice and applications — This survey aims to provide a comprehensive summary of the state-of-the-art security solutions for SMPC. Before proceeding with the descriptions of the individual schemes and their properties, we present the general framework in Section 2, including basic concepts, research areas, security requirements, and various building blocks.Generic constructions for secure computation, including secure ...
- Concretely efficient secure multi-party computation ... - SciEngine — Secure multi-party computation (MPC) allows a set of parties to jointly compute a function on their private inputs, and reveals nothing but the output of the function. In the last decade, MPC has rapidly moved from a purely theoretical study to an object of practical interest, with a growing interest in practical applications such as privacy-preserving machine learning (PPML).
- A Pragmatic Introduction to Secure Multi-Party Computation — Secure multi-party computation (MPC) has evolved from a theoretical curiosity in the 1980s to a tool for building real systems today. ... This book introduces several important MPC protocols, and surveys methods for improving the efficiency of privacy-preserving applications built using MPC. Besides giving a broad overview of the field and the ...
- PDF Secure Multi-Party Computation for Machine Learning: A Survey — Thus, each party's data remains secure and private, yet a meaningful, collective computation can still take place. While several survey papers on Secure Multi-Party Com-putation (SMPC) have been published [7]-[11], only a subset offers a comprehensive overview of the field. Furthermore, certain papers, such as [7], [8], fall short of ...
- PDF Multiparty Computation, an Introduction - Aarhus Universitet — These lecture notes introduce the notion of secure multiparty computation. We in-troduce the universal composition framework for phrasing and proving security about protocols, and survey some known general results that describe when secure multi-party computation is possible. We then look at some general techniques for building
- PDF Concretely efficient secure multi-party computation protocols: survey ... — Secure multi-party computation (MPC) allows a set of parties to jointly compute a function on their private inputs without revealing anything but the output of the function. Speci cally, MPC allows n parties to jointly compute the following function: (y 1;:::;y n) f(x 1;:::;x n); where every party P iholds an input x i, obtains an output y
6.3 Open-Source Libraries and Tutorials
- Multi-Party Computation: Scalability and Accessibility — Researchers at Boston University, together with collaborators at several other institutions and organizations, are developing open-source libraries, frameworks, and systems that enable the implementation and deployment of applications that employ secure multi-party computation in accessible and scalable ways. Please contact us if you would like to learn more or are interested in collaborating.
- Secure Multi-Party Computation | SpringerLink — Secure Multi-Party Computation enables a group of parties to compute a function while jointly keeping their private inputs secret. The chapter discusses the definition of secure multi-party computation, its benefits and drawbacks, and its potential applications.
- PDF MOTION - A Framework for Mixed-Protocol Multi-Party Computation - IACR — We present MOTION, an eficient and generic open-source framework for mixed-protocol secure multi-party computation (MPC). MOTION is built in a user-friendly, modular, and extensible way, intended to be used as a tool in MPC research and to increase adoption of MPC protocols in practice. Our framework incorporates several important engineering decisions such as full communication serialization ...
- GitHub - rdragos/awesome-mpc: A curated list of multi party computation ... — A Pragmatic Introduction to Secure Multi-Party Computation - A broad introduction to the field of secure multi-party computation, covering both the fundamental constructions and many of the recent improvements. The book emphazises the intuition and ideas behind the protocols rather than rigorous proofs.
- Secure Multi-Party Computation for Collaborative Data Analysis in ... — Within the scope of this research, we provide a Secure Multi-Party Computation (SMPC) architecture that has been adapted specifically for the purpose of collaborative data analysis in network protection. Significant improvements have been made to the framework in terms of performance metrics, security, and applicability in the real world. When measured against a baseline, comparative analysis ...
- GitHub - cryptobiu/libscapi: Comprehensive Open Source Library for ... — libscapi is the Open source C++ library for implementing high performance secure two-party and multiparty computation protocols (SCAPI stands for the "Secure Computation API"). It provides a reliable, efficient, and highly flexible cryptographic infrastructure. Libscapi is developed by Bar Ilan University Cryptography Research Group.
- Secure Multiparty Generative AI - arXiv.org — We propose a Secure Multi-Party Computation (SMPC) ar-chitecture for transformer-based generative AI models. This ensures user input privacy and model intellectual property protection by securely sharding the model across multiple servers in a decentralized network.
- Secure Multiparty Computation via Homomorphic Encryption Library — Secure multiparty computation (MPC) is required when individuals want to privately evaluate a function over their inputs. While evaluating a common function, the participants do not reveal their inputs to each other. A homomorphic encryption (HE) scheme allows the evaluation of arbitrary computations on encrypted data without decrypting it. In theory, realizing MPC through a HE scheme is a ...
- (PDF) Secure Multi-Party Computation (MPC): Privacy-preserving ... — Secure Multi-Party Computation (MPC) is a vital field of research that focuses on developing privacy-preserving protocols for collaborative computation. In the context of artificial intelligence ...
- multi-party-computation · GitHub Topics · GitHub — Minimal pure-Python implementation of a secure multi-party computation (MPC) protocol for evaluating arithmetic sum-of-products expressions via a non-interactive computation phase.